TRUST CENTER
Trust is the foundation of every event
Companies use the MICE Portal to manage their event procurement, including data on participants, quotes, and invoices. Here you can see how we protect this data, what evidence we have, and what documents you can request.

Privacy Policy
What personal data we process on our website and platform, and what rights you have.
Data Processing Agreement
Our model data processing agreement (DPA) pursuant to Article 28 of the GDPR for all customers who process data from employees and participants via the MICE Portal.
Service Provider
We review every service provider before they begin work and on a regular basis thereafter. We enter into a contract with all parties that process data on our behalf in accordance with Article 28 of the GDPR. Customers receive this list along with the General Terms and Conditions.
Data Storage
Our hosting partner, makandra GmbH, operates the platform and databases at the noris network data center near Munich. Transfers to third countries are permitted only with safeguards in accordance with Art. 44 et seq. of the GDPR.
Technical and Organizational Measures
Our TOMs under Article 32 of the GDPR describe controls for access, use, and disclosure.
Data Protection Officer
Our external data protection officer can be reached at privacy@miceportal.com.
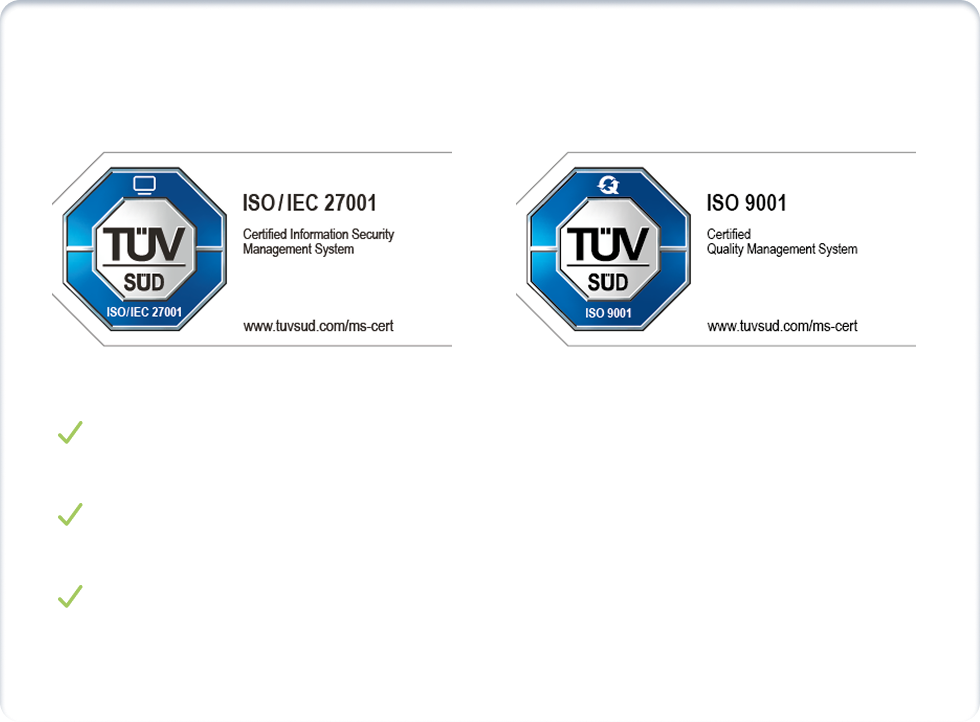
ISMS in accordance with ISO/IEC 27001
Certified by TÜV SÜD under ISO/IEC 27001:2022 for the development, maintenance, and IT operations of our SaaS solutions.
Single Sign-On
Your employees log in via their own identity provider using SAML 2.0.
Roles and Rights
Your administrators control who can view which projects, offers, and invoices. Internally, we follow the "need-to-know" principle, with regular reviews of access rights.
Encryption
Data is transmitted via TLS 1.2 or higher. Stored data and backups are kept on fully encrypted storage media.
Penetration Tests
At least once a year by a certified external service provider. Clients receive the results under an NDA.
Monitoring and Logs
The infrastructure is monitored around the clock. Access to systems is logged, and the logs are retained.
Hosting in Germany
Highly available infrastructure at the noris network data center near Munich, operated by makandra GmbH.
Daily Backups
Encrypted and stored in a separate fire compartment in Germany. We test the recovery process regularly.
Emergency Plan
A documented business continuity and disaster recovery plan, tested at least once a year, including in collaboration with our hosting partner.
Report a Vulnerability
Have you found a security vulnerability? Please report it to info@miceportal.com. We will respond within 3 business days.
Legal Notice
MICE Portal GmbH, Registration Information and Authorized Representatives.
November 11, 2026
Trust Center Published
All documentation regarding data protection and security in one place.
June 20, 2026
The entire platform is hosted by a hosting partner in Germany
The entire operation is hosted by makandra GmbH at the noris network data center near Munich.
February 23, 2026
ISO/IEC 27001:2022 Certificate
TÜV SÜD has certified our ISMS in accordance with the current standard.
Have you subscribed to our newsletter yet?
Stay up to date and receive regular updates on the latest trends and developments in the MICE industry.
Where is our data stored?
Our hosting partner, makandra GmbH, operates the platform, databases, and backups at the noris network data center near Munich, Germany.
What certifications does your hosting provider have?
makandra has been audited in accordance with TISAX. The noris network data center is certified to ISO/IEC 27001, EN 50600, and ISAE 3402 Type II, among other standards.
Is our data encrypted at rest?
Yes. All data storage on the platform is fully encrypted. This also applies to the backups.
How is data protected during transmission?
All connections to the platform are encrypted using TLS 1.2 or higher.
How often do you back up our data?
Daily. The backups are encrypted and stored in a separate fire compartment in Germany. We test the recovery process regularly.
What happens if the data center goes down?
We have a documented plan for business continuity and disaster recovery. We test it at least once a year, including in collaboration with our hosting partner.
How often are penetration tests conducted?
At least once a year by a certified external service provider. We make the results available to clients under an NDA. In-house testing is possible upon prior agreement.
Does the MICE Portal support single sign-on?
Yes, via SAML 2.0 with your own identity provider.
Who at MICE Portal has access to our data?
Only employees who need it for their work. We grant permissions on a role-based basis and review them regularly. Multi-factor authentication is required for systems containing sensitive data.
How do you notify us in the event of a security incident?
We notify affected customers immediately in accordance with our incident response process and the provisions of the General Terms and Conditions (AVV). We report reportable incidents to the regulatory authority within 72 hours.
What happens to our data after the contract ends?
Upon request, we will return your data. We will then delete it within 30 days; backups expire no later than 7 days after creation. This does not apply to data subject to legal retention requirements, such as invoices. You can receive a deletion log upon request.
How do you train your employees?
All employees are contractually bound to maintain confidentiality, protect data, and ensure information security. They receive training upon joining the company, followed by regular awareness training sessions and annual data protection training.
Will you complete our security questionnaire?
Yes. Please submit it through the "Request Documents" page. You can find many answers right here in the Trust Center.
Do you have any questions about security or data protection?
Our ISMS team can assist with audits, questionnaires, and contract reviews.